Monitoring object
What a monitoring object is, how it helps detect a DDoS attack, and why there may be several objects.
What it is
A monitoring object is a set of traffic threshold values defined for your IP addresses or subnets.
In simple terms, it is the limit of acceptable load: which traffic volume is considered normal and which is considered a DDoS attack.
How it works
A monitoring object is a configuration for the analysis system. The system works with it as a sensor:
-
It continuously analyzes traffic to the specified IP addresses or subnets at the L3/L4 layers.
-
It compares the traffic volume with the defined thresholds.
-
If a threshold is exceeded, it signals a network anomaly.
This is how the protection identifies where normal traffic ends and a DDoS attack begins.
What it consists of
One monitoring object includes:
-
The name of the protected resource. You can see it in the management console. It usually combines the name of an infrastructure segment and a service. For example:
company_dns,company_sip, orcompany_nat. -
The IP addresses or subnets that need protection.
-
Detection thresholds. Rules that the system uses to identify an anomaly. Each threshold combines:
-
Traffic calculation type. It defines how the system calculates load: for the whole monitoring object (
global), separately for each IP address (local), or for groups of addresses (subnet). -
Attack vector. It specifies which protocol, port, or packet flag the system uses to analyze traffic (for example,
tcp-syn-flood,dns-flood,udp-flood, orip-fragment-flood). -
Static limit. A value in
bytesorpackets; exceeding it means that the load is considered abnormal.
-
Example object:
name: company_main                   # Object name
cidrs:
  - 192.0.2.0/24                     # Destination IP addresses
rules:                               # Threshold block
  - type:
      - global                       # Calculation type
    units:
      - bytes                        # Units
    vectors:
      - dns-flood                    # Vector
    limit-threshold: 100000000       # Static limit
How it is created
Our engineers create and configure monitoring objects when connecting protection, so you do not need to configure them yourself.
The process has three stages.
1. Completing the questionnaire
Complete the questionnaire sent by our engineers. A list of IP addresses or subnets is the minimum information that you need to provide so that we can create the objects and enable protection.
If you have specific traffic or special limits, include them in the questionnaire. This helps us configure protection for your resource from the start, so it does not identify sudden spikes in normal load as an attack.
2. Determining the number of objects
Based on your information, we group IP addresses into monitoring objects. The main criterion is traffic volume:
-
If the load on all your resources is roughly the same, we group them into one monitoring object and define a common threshold based on total traffic.
-
If the load on some services is significantly different from the others, we create separate objects and configure individual thresholds for them.
Let us look at an example of why several monitoring objects may be needed.
Suppose you have a website and an email server. Under normal conditions, the peak legitimate traffic to your website reaches 5,000 packets per second, while the email service reaches 100 packets per second. If they are combined into one monitoring object, the detection threshold must be calculated as follows: add their peak loads (5,000 + 100 = 5,100) and add 10–15%. This produces a threshold of about 5,600–5,900 packets per second.
In this scenario, if someone starts attacking the email service at a rate of 1,000 packets per second, the combined traffic to the website and email service will usually not reach the 5,600–5,900 threshold. The protection will not detect or block the attack.
For this reason, we divide the website and email service into two monitoring objects:
-
Website: a threshold of 5,500–5,800 packets per second.
-
Email service: a threshold of about 150 packets per second.
As a result, if an attack on the email service reaches 1,000 packets per second, the analysis system detects it and the protection blocks the attack traffic.
| We usually create separate monitoring objects for high-load NAT addresses and low-traffic services, such as email, DNS, and SIP gateways. |
3. Setting detection thresholds
At this stage, we set a detection threshold for each monitoring object.
If you specify limits for your services in the questionnaire, we take them into account when configuring thresholds.
In other cases, we use a proven method: during the first week after protection is connected, we monitor traffic to your subnets and record actual load peaks. We then set final thresholds with a margin of approximately 10–15% above the maximum value for that period.
This buffer reduces the risk of false positives. If you expect unusually high traffic on certain dates, for example on Black Friday, contact support in advance. The engineers will adjust the thresholds for the expected load so that protection works correctly.
If you notice degradation of legitimate traffic or attacks getting through, contact support. Our engineers will promptly adjust the settings.
How it helps mitigate attacks
The analysis system uses monitoring objects as a reference: it compares the current load on your IP addresses with the defined thresholds to distinguish normal traffic from a DDoS attack.
How it works: the analysis system uses sampling. It does not process the entire data flow but receives only a copy of it—one packet out of every 250. This makes it possible to see the situation in real time without loading the network.
The analysis system compares the received data with monitoring object settings and determines where to route the traffic: directly to your IP addresses or to the mitigation system.
Below, we explain this process using an object with a threshold of 40,000 packets per second (pps) for UDP traffic.
Normal operation
-
The analysis system receives packet samples and sees that the load on the object’s IP addresses is 20,000 pps.
-
The object tells the analysis system that this load is safe and normal for these addresses.
-
Traffic to the object’s IP addresses goes directly to them.
-
The analysis system records the metrics and monitors the situation without interfering with the network.
Anomaly detection
-
The analysis system detects that the load on the object’s IP addresses has risen to 100,000 pps.
-
It compares the value with the object’s threshold of 40,000 pps and identifies an attack.
-
It instructs the router to send the traffic flow to the mitigation system. The change takes up to one second.
-
The mitigation system filters out malicious packets.
-
Clean traffic reaches the destination IP addresses.
End of an anomaly
-
The analysis system sees that the load has fallen back to 20,000 pps.
-
It waits for some time to confirm that the metrics are stable.
-
It detects that the attack has ended and instructs the router to send traffic directly to the object’s IP addresses.
-
It returns to standby mode and continues monitoring.
Working with an object
All monitoring objects are available in the management console under Network protection → Monitoring objects.
Each object has a basic overview:
-
IDis the unique identifier of the object in the system. -
Nameis the name of the protected object. -
IPsare the addresses or subnets assigned to this object and under protection.
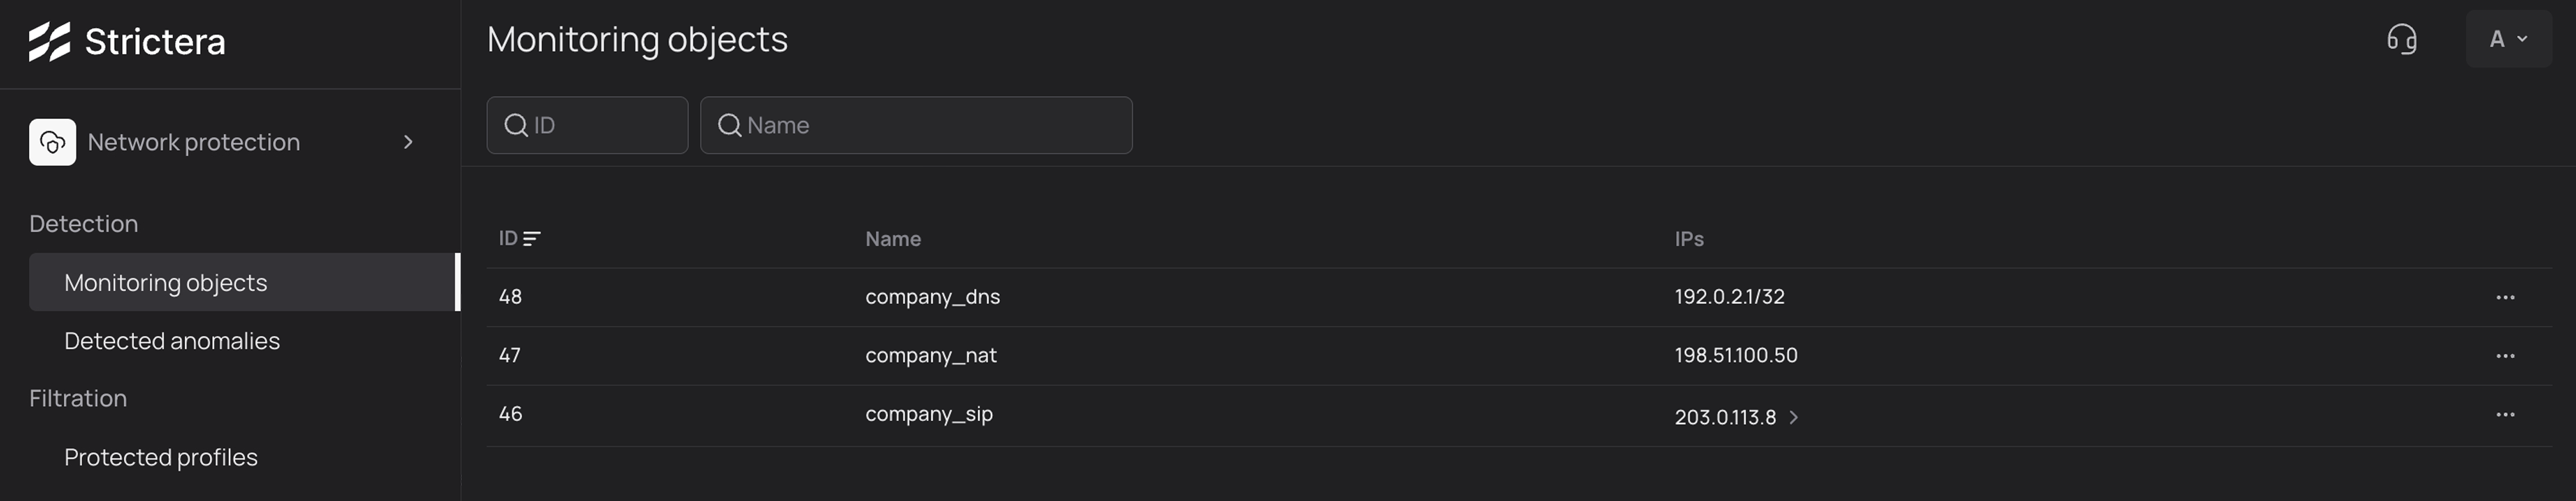
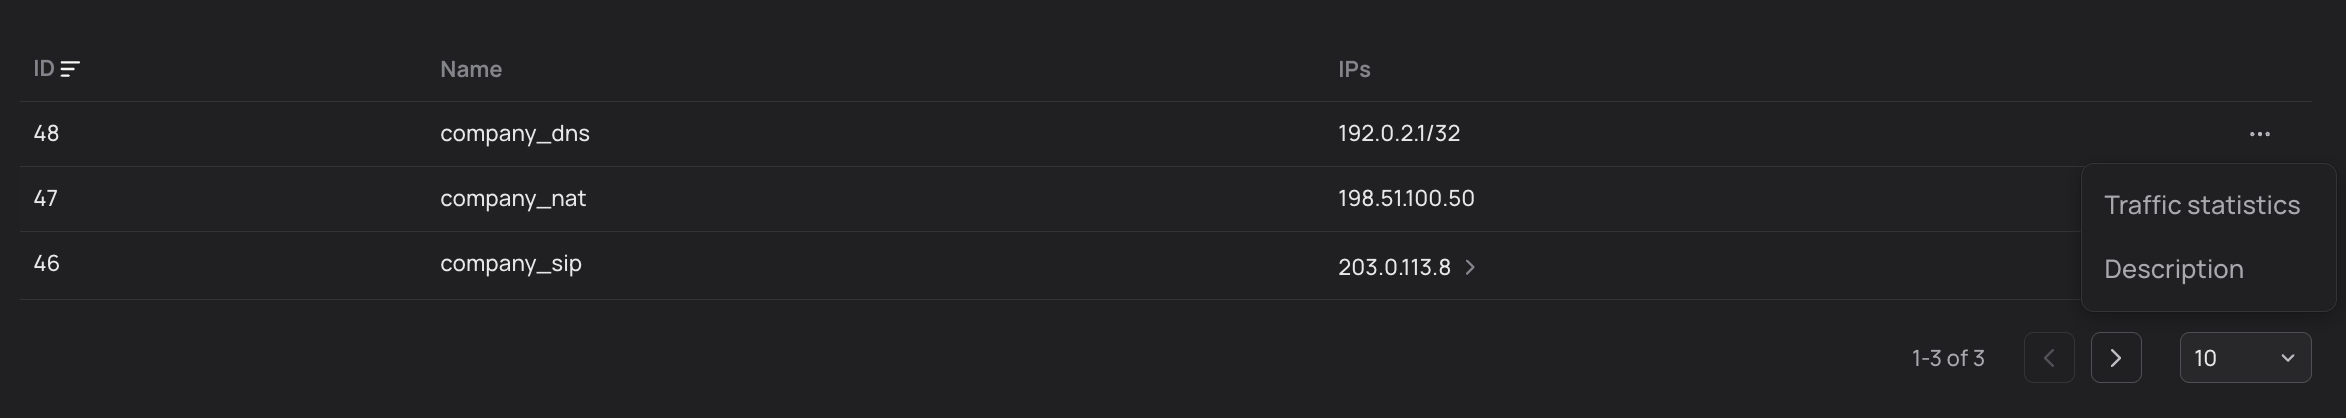
All work with an object is done through the menu, which opens when you select the ellipsis (…) at the end of the row. It contains two tools:
-
Traffic statisticsis a section for monitoring network activity. Here, you can view real-time load charts. For more information, see Monitoring object traffic statistics. -
Descriptionis a text note. Specify the purpose of the object so that you can find it easily in the list.